Know Your Supplier, built for the factory floor.
A manufacturer onboards hundreds of vendors: the company supplying engines, the one supplying glass, the one supplying seats. Every one is a corporate entity that has to be verified. Compliable.ai runs that screening at volume on the same architecture that clears an energy trading desk, and presses harder on the suppliers that warrant it.
Hundreds of vendors. Every one is a due-diligence question.
A manufacturer's risk does not sit with the customer. It sits with the supply chain. Every vendor is a legal entity that could be sanctioned, hiding its real owners, or carrying reputational risk that becomes yours the moment you buy from it. Compliable.ai makes that chain visible, scores every link, and lets you set how hard each one is checked.
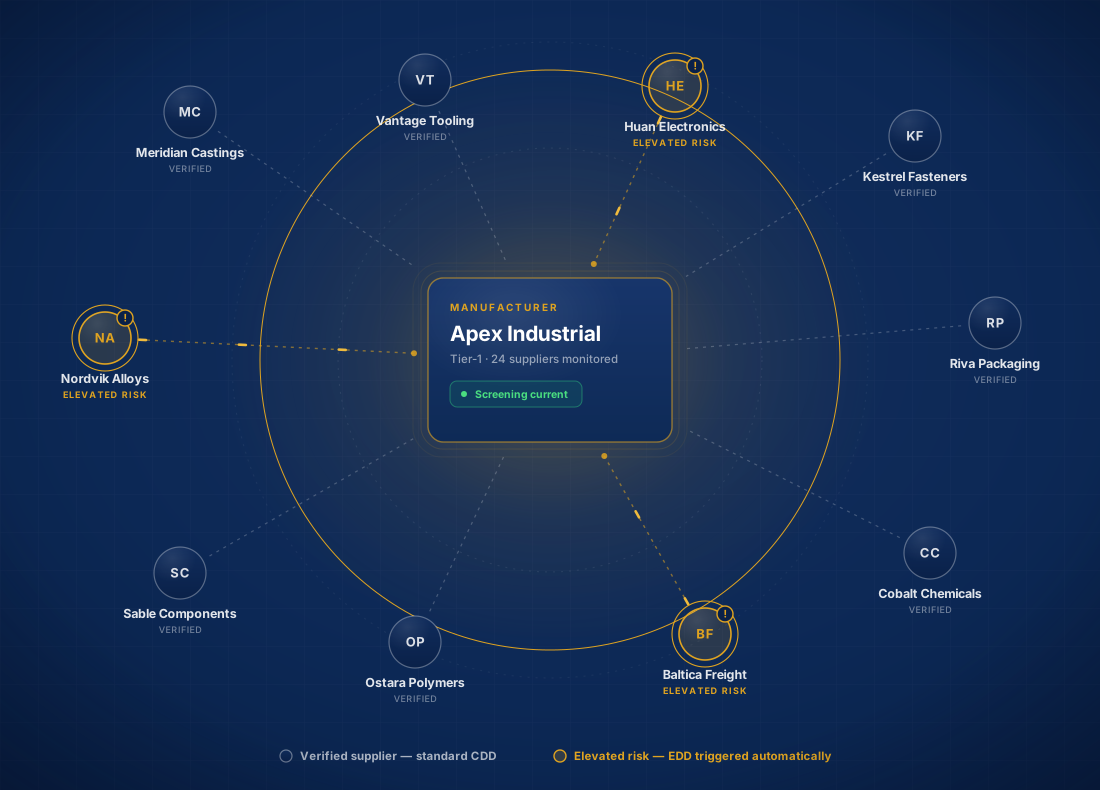
Hundreds of entities to verify
A single assembly program can pull in hundreds of parts suppliers. Each one is a company that needs onboarding, verification, and periodic review.
Not every supplier is equal
Most clear under standard customer due diligence. The few that show elevated risk, three of ten here, trigger enhanced due diligence automatically, on the thresholds you set. The windshield vendor is not the chemical supplier.
The record has to hold
Trade compliance, anti-money-laundering (AML) exposure, and sanctions all reach into procurement. Screening continues after onboarding, and an auditor can ask about any of it.
The same three questions, asked of every vendor. You configure how each is answered.
Who is this supplier, what is the risk, and can you defend the call. Compliable.ai answers all three on the same platform that clears an energy desk, and every part is yours to set: the documents you require, the checks you run, the steps you keep or cut, and what happens at each event. Below is the default flow for a manufacturing vendor. Reshape it to your process.
Request
Procurement adds a vendorCollect
Registration & certsScreen
Sanctions, PEP, mediaValidate
AI document checksAssess
Tier & risk bandAuthorize
Approve the vendorMonitor
Certs & re-screeningCollect
- Corporate registration and incorporation papers
- Ownership and control records for beneficial-owner tracing
- Tax identification number (TIN) and trade licenses
- Quality, safety, or origin certifications where the part requires them
Screen
- Corporate identity and ultimate beneficial owner (UBO) verification via GLEIF
- Sanctions and watchlist screening across the Office of Foreign Assets Control (OFAC), World-Check, and Dow Jones
- Politically exposed person (PEP) via Wikidata, adverse media via GDELT
- Optional criminal background check on key individuals for sensitive roles
Decide
- Evidence measured against your procurement and compliance policy
- Open questions answered before a vendor is activated
- A recommendation with the reasoning shown
- A closed, encrypted audit trail attached to the supplier record
The standard documents, validated today. The rest, configured with you.
Compliable.ai validates the critical documents every counterparty shares out of the box: articles of formation and incorporation, standard bank documents, and tax forms. The documents and checks specific to your vendors and suppliers you give us as examples, and we turn them into validation and workflow with you, not in an engineering backlog. For the parts unique to your desk, we partner and refine against your real cases.
The AI does the gathering. Your analyst makes the call.
Every supplier file runs through the same set of AI capabilities that power a trading-desk onboarding. Here is what that looks like pointed at a vendor.
Document validation
Reads a vendor's registration, tax forms, and certifications in seconds, extracts the entity name, identifiers, and address, and flags a bad or expired document on upload.
Cross-document analysis
Checks the whole supplier file for contradictions. If the name on the tax form does not match the incorporation papers, or the address is inconsistent, it surfaces immediately.
Website review
Scans the supplier's own website for consistency with what they filed, and for red flags a procurement team would want to know before the first purchase order.
Screening triage
Runs multi-provider screening on the entity and its owners, then scores false-positive probability so a common surname does not stall an approval.
Enrichment linking
Matches the vendor across open data sources for corporate structure, ownership, leaked-document exposure, and adverse media, and links what belongs together.
Executive summary
Writes the full supplier onboarding into a defensible record in seconds, ready for the approve-or-hold decision with the audit trail attached.
Press lightly on routine vendors. Press hard where it matters.
Not every supplier earns the same review. Compliable.ai scores each vendor and tiers them, so the windshield supplier clears quickly and the safety-critical or foreign-owned supplier gets the deeper look, automatically, by rule.
Standard commodity vendors
Low-risk, easily substituted parts. Identity, sanctions, and ownership screening at baseline depth.
Critical or single-source parts
Safety-relevant or hard-to-replace components. Adds enhanced ownership tracing and adverse-media review.
High-risk or foreign-owned
Sanctioned-jurisdiction exposure or opaque ownership. Full enhanced due diligence (EDD) and optional individual background checks.
The same four agents, pointed at your vendors.
Agentic Authority is not one AI making calls. It is specialized agents, each doing one job, collaborating through a controlled workflow, here configured for supplier onboarding.
Document Intelligence Agent
Reads and validates every supplier document as it uploads, and cross-checks the file. A registration that does not match the entity name, or a missing certification, surfaces the moment the file lands.
Agentic Screening Agent
Runs sanctions, watchlist, politically exposed person, and adverse-media screening on the vendor and its owners in one pass, then explains and scores each hit and enriches confirmed matches.
Signal Agent
Applies your procurement policy and the vendor's risk tier to the evidence, then recommends the call: approve, hold, or escalate, with the reasoning shown.
Executive Synthesis Agent
Writes the full supplier onboarding into a defensible record, ready for the approve-or-hold decision, with the audit trail attached for any future review.
A verified supplier becomes a profile the whole network can reuse.
Each completed onboarding turns into a compliance profile the supplier controls and can share. The next manufacturer that needs that vendor starts ahead, collecting only the delta instead of the whole file. Fewer repeat requests for the supplier, faster activation for you.
Compliance does not stop at approval. Neither does the platform.
Most tools go quiet once a vendor is onboarded. Compliable.ai keeps watching, so an expired certification or a new sanctions hit becomes an alert, not a surprise in an audit.
Conditions & expirations
Certifications, insurance, and document renewals are tracked with due dates. The team is alerted before anything lapses, and optionally so is the supplier.
Periodic re-screening
Active vendors are re-screened on a schedule you set. A supplier that clears today and appears on a list next quarter is caught automatically.
Renewal without restart
When an annual review comes due, the system opens a new cycle, but the vendor's existing documents and data carry forward. They only provide what actually changed.
Onboard your supply chain, at volume.
We will run one of your vendor types through the manufacturing template, from document upload to a defensible decision, in a live walkthrough.